Day-to-day operations
Managed IT & Cybersecurity
Someone watching it, and someone answering when it breaks.
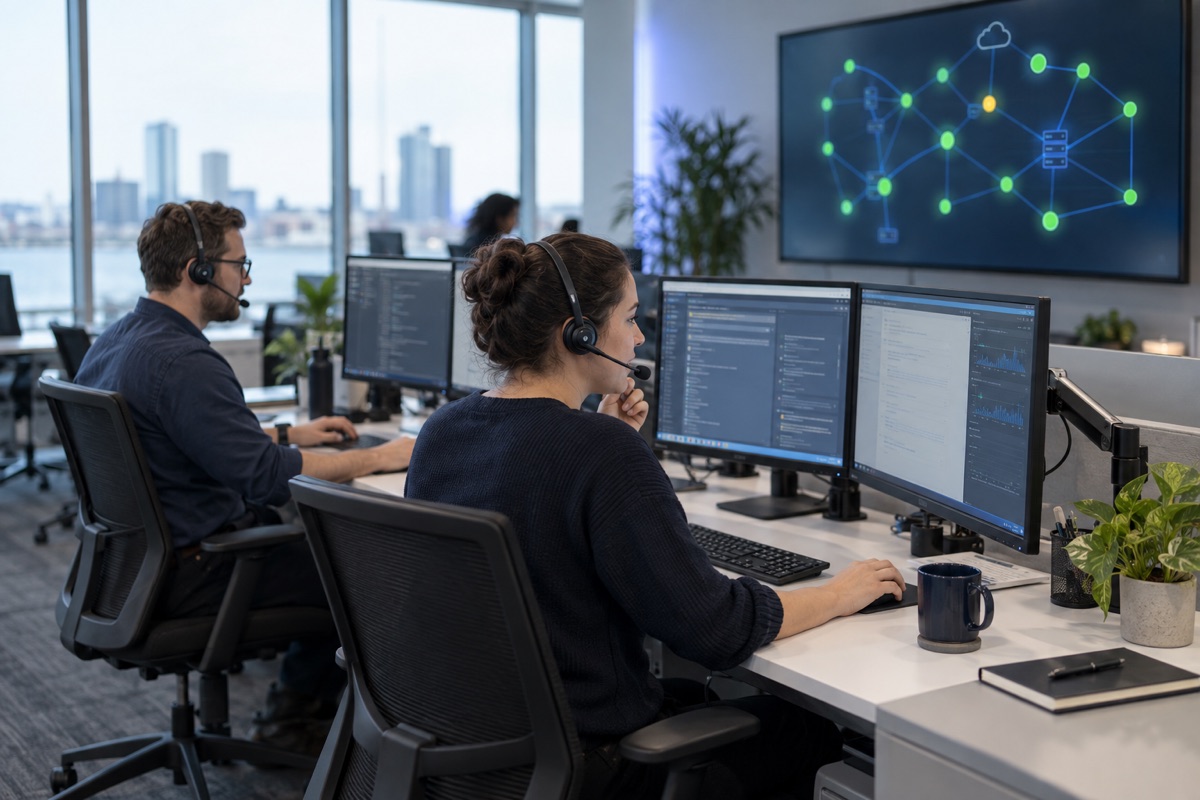
A managed service provider with a 24/7 NOC, a staffed service desk, and a security baseline your cyber insurer will accept, for a flat monthly price per seat.
What's included
One managed services agreement covers the whole environment.
Service desk & helpdesk
A staffed service desk with ticketing, so every request is logged, given a priority, and closed with a note. Remote first, with on-site dispatch when remote will not cut it.
Remote monitoring & management
An RMM agent on every workstation and server reports health, runs maintenance, and raises a ticket in our NOC before your staff notice anything.
Endpoint detection & response
EDR on every device with managed detection and response behind it: alerts reviewed by people around the clock, and isolation actions agreed in advance.
Identity & access management
Enforced MFA, conditional access, least-privilege admin accounts, and a documented onboarding and offboarding process for every user.
Backup & disaster recovery
Local and cloud copies, including an immutable copy an attacker cannot delete, restores tested on a schedule, and a recovery time objective agreed in writing.
Email security & awareness training
Filtering for phishing, impersonation, and payment fraud, plus security awareness training and phishing simulations so staff recognize what gets through.
Microsoft 365 & cloud administration
Licensing, migration, and tenant hygiene: a security baseline applied to the tenant, accounts closed the day someone leaves, and nonprofit pricing where you qualify.
Patch management & lifecycle
Operating system, third-party application, and firmware patching on a schedule, with a hardware refresh plan you can budget three years out.
vCIO reviews & documentation
A business review of ticket trends, security posture, and the technology roadmap on a cadence set by your tier, and a documentation platform holding your passwords, diagrams, and runbooks. All of it is yours if you leave.
Who this is for
Organizations without an IT department, and IT directors who need a co-managed bench.
Every industry we serve pulls on this area differently. Jump to yours to see what it usually looks like.
How engagements run
No mystery scope, no surprise change orders.
- 01
Walk it
We look at the space, the stack, or the drawing set before quoting anything.
- 02
Scope it
A fixed written scope: what is included, what is not, who does what, and when.
- 03
Run it
One project manager owns it end to end and stays your contact after handoff.
What does managed IT cost?
Flat monthly per seat, tiered by whether you need service desk and monitoring only or the full security stack with EDR, backup, and 24/7 response. Quotes are firm after a short discovery call.
Do we have to move everything at once?
No. Most clients start with security and backup, then move the service desk over once the first month is quiet.
How fast can someone help?
Every ticket gets a priority and a response target from the service level agreement in your contract. The targets depend on your tier and location, and they are written down, not implied.
What happens during onboarding?
Discovery documents every device, account, circuit, and vendor. Monitoring, EDR, and backup agents go on every machine, every password the previous provider held is rotated, and support cuts over on an agreed date. A 30-day review closes it out.
Do you offer co-managed IT?
Yes. If you have an IT person or team, we supply the tooling (RMM, EDR, backup, ticketing), the after-hours coverage, and an escalation path, and your staff keep ownership of the environment.
Do you follow a security framework?
Our security baseline is aligned to CIS Controls v8.1 Implementation Group 1 and mapped to NIST CSF 2.0, and we can show which control each tool covers. We do not claim certification, and we will not claim compliance on your behalf. Your auditor or insurer decides that; we supply the evidence.
What reporting do we get?
A monthly report covering tickets, patch status, backup results, and security alerts, plus a business review of risks and the roadmap on a cadence set by your tier.
Tell us what's in front of you.
A drawing set, a failing switch, an audit deadline, or a hunch that IT costs too much. We'll tell you who picks it up and what it takes.